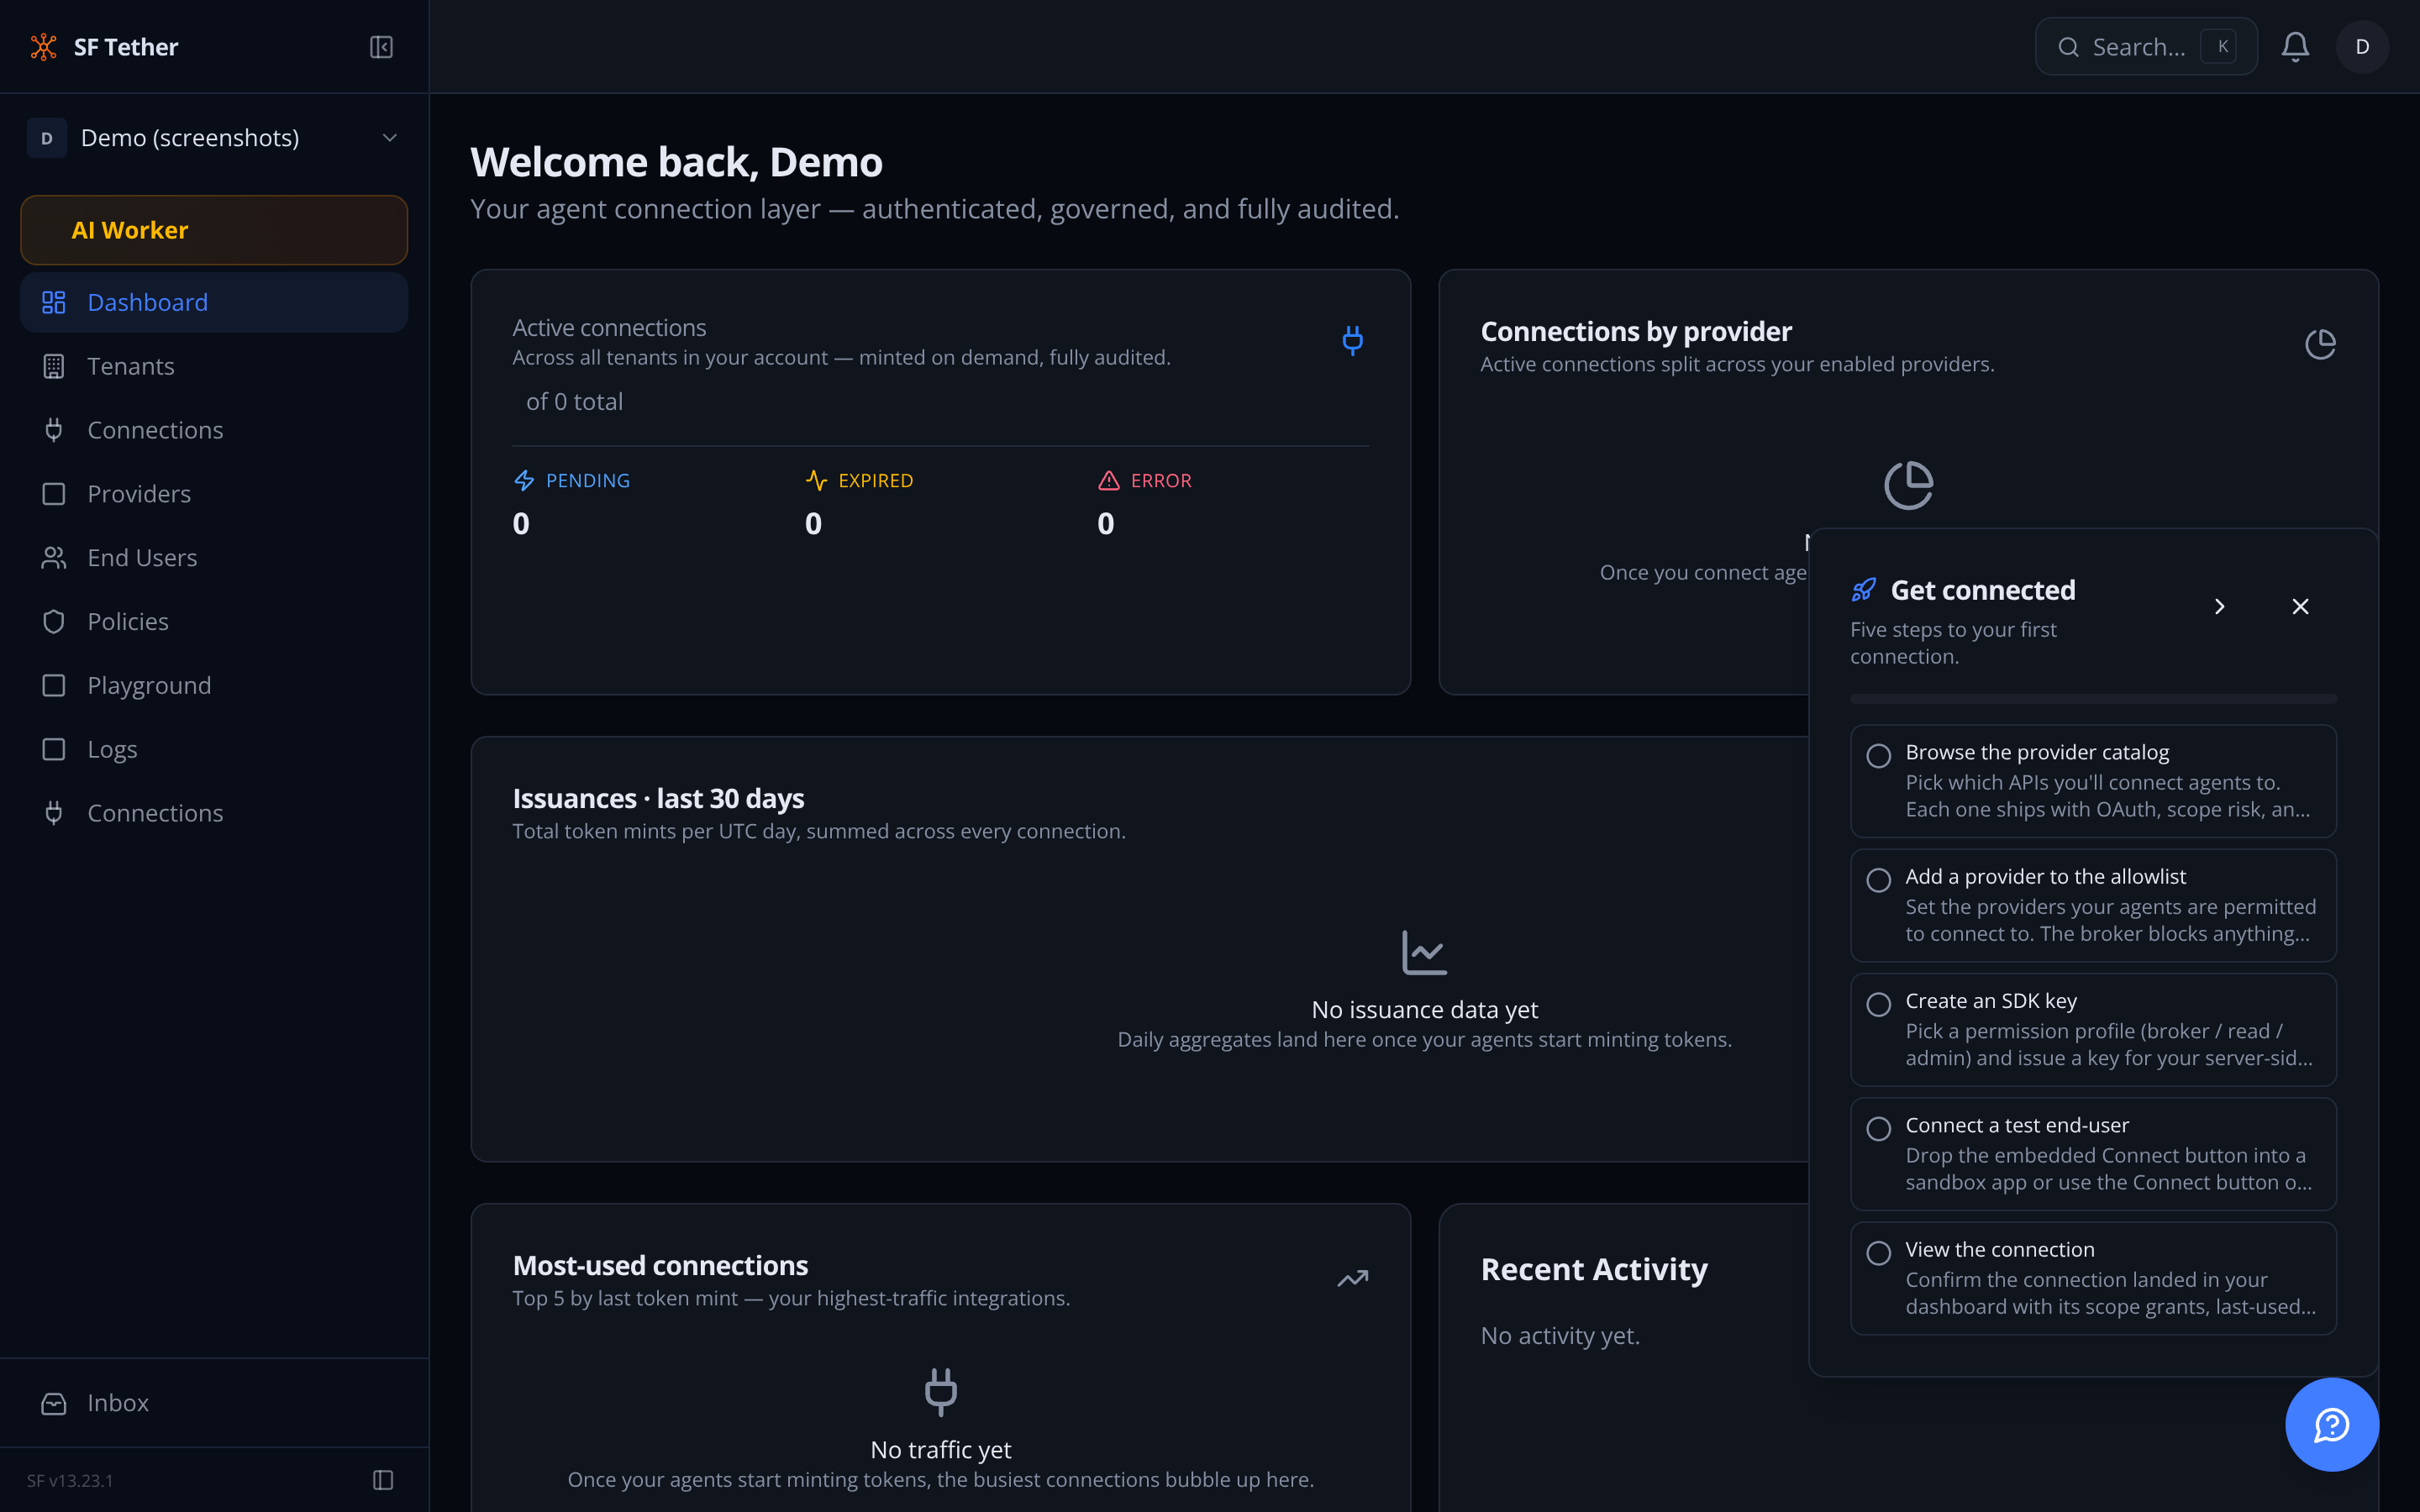
Your agents reach the entire internet. Authenticated.
SF Tether handles OAuth flows, token vaulting, scope enforcement, and automatic refresh for every provider in the catalog — so your agents get a valid, least-privilege token in one SDK call, with a full audit trail behind every issuance.
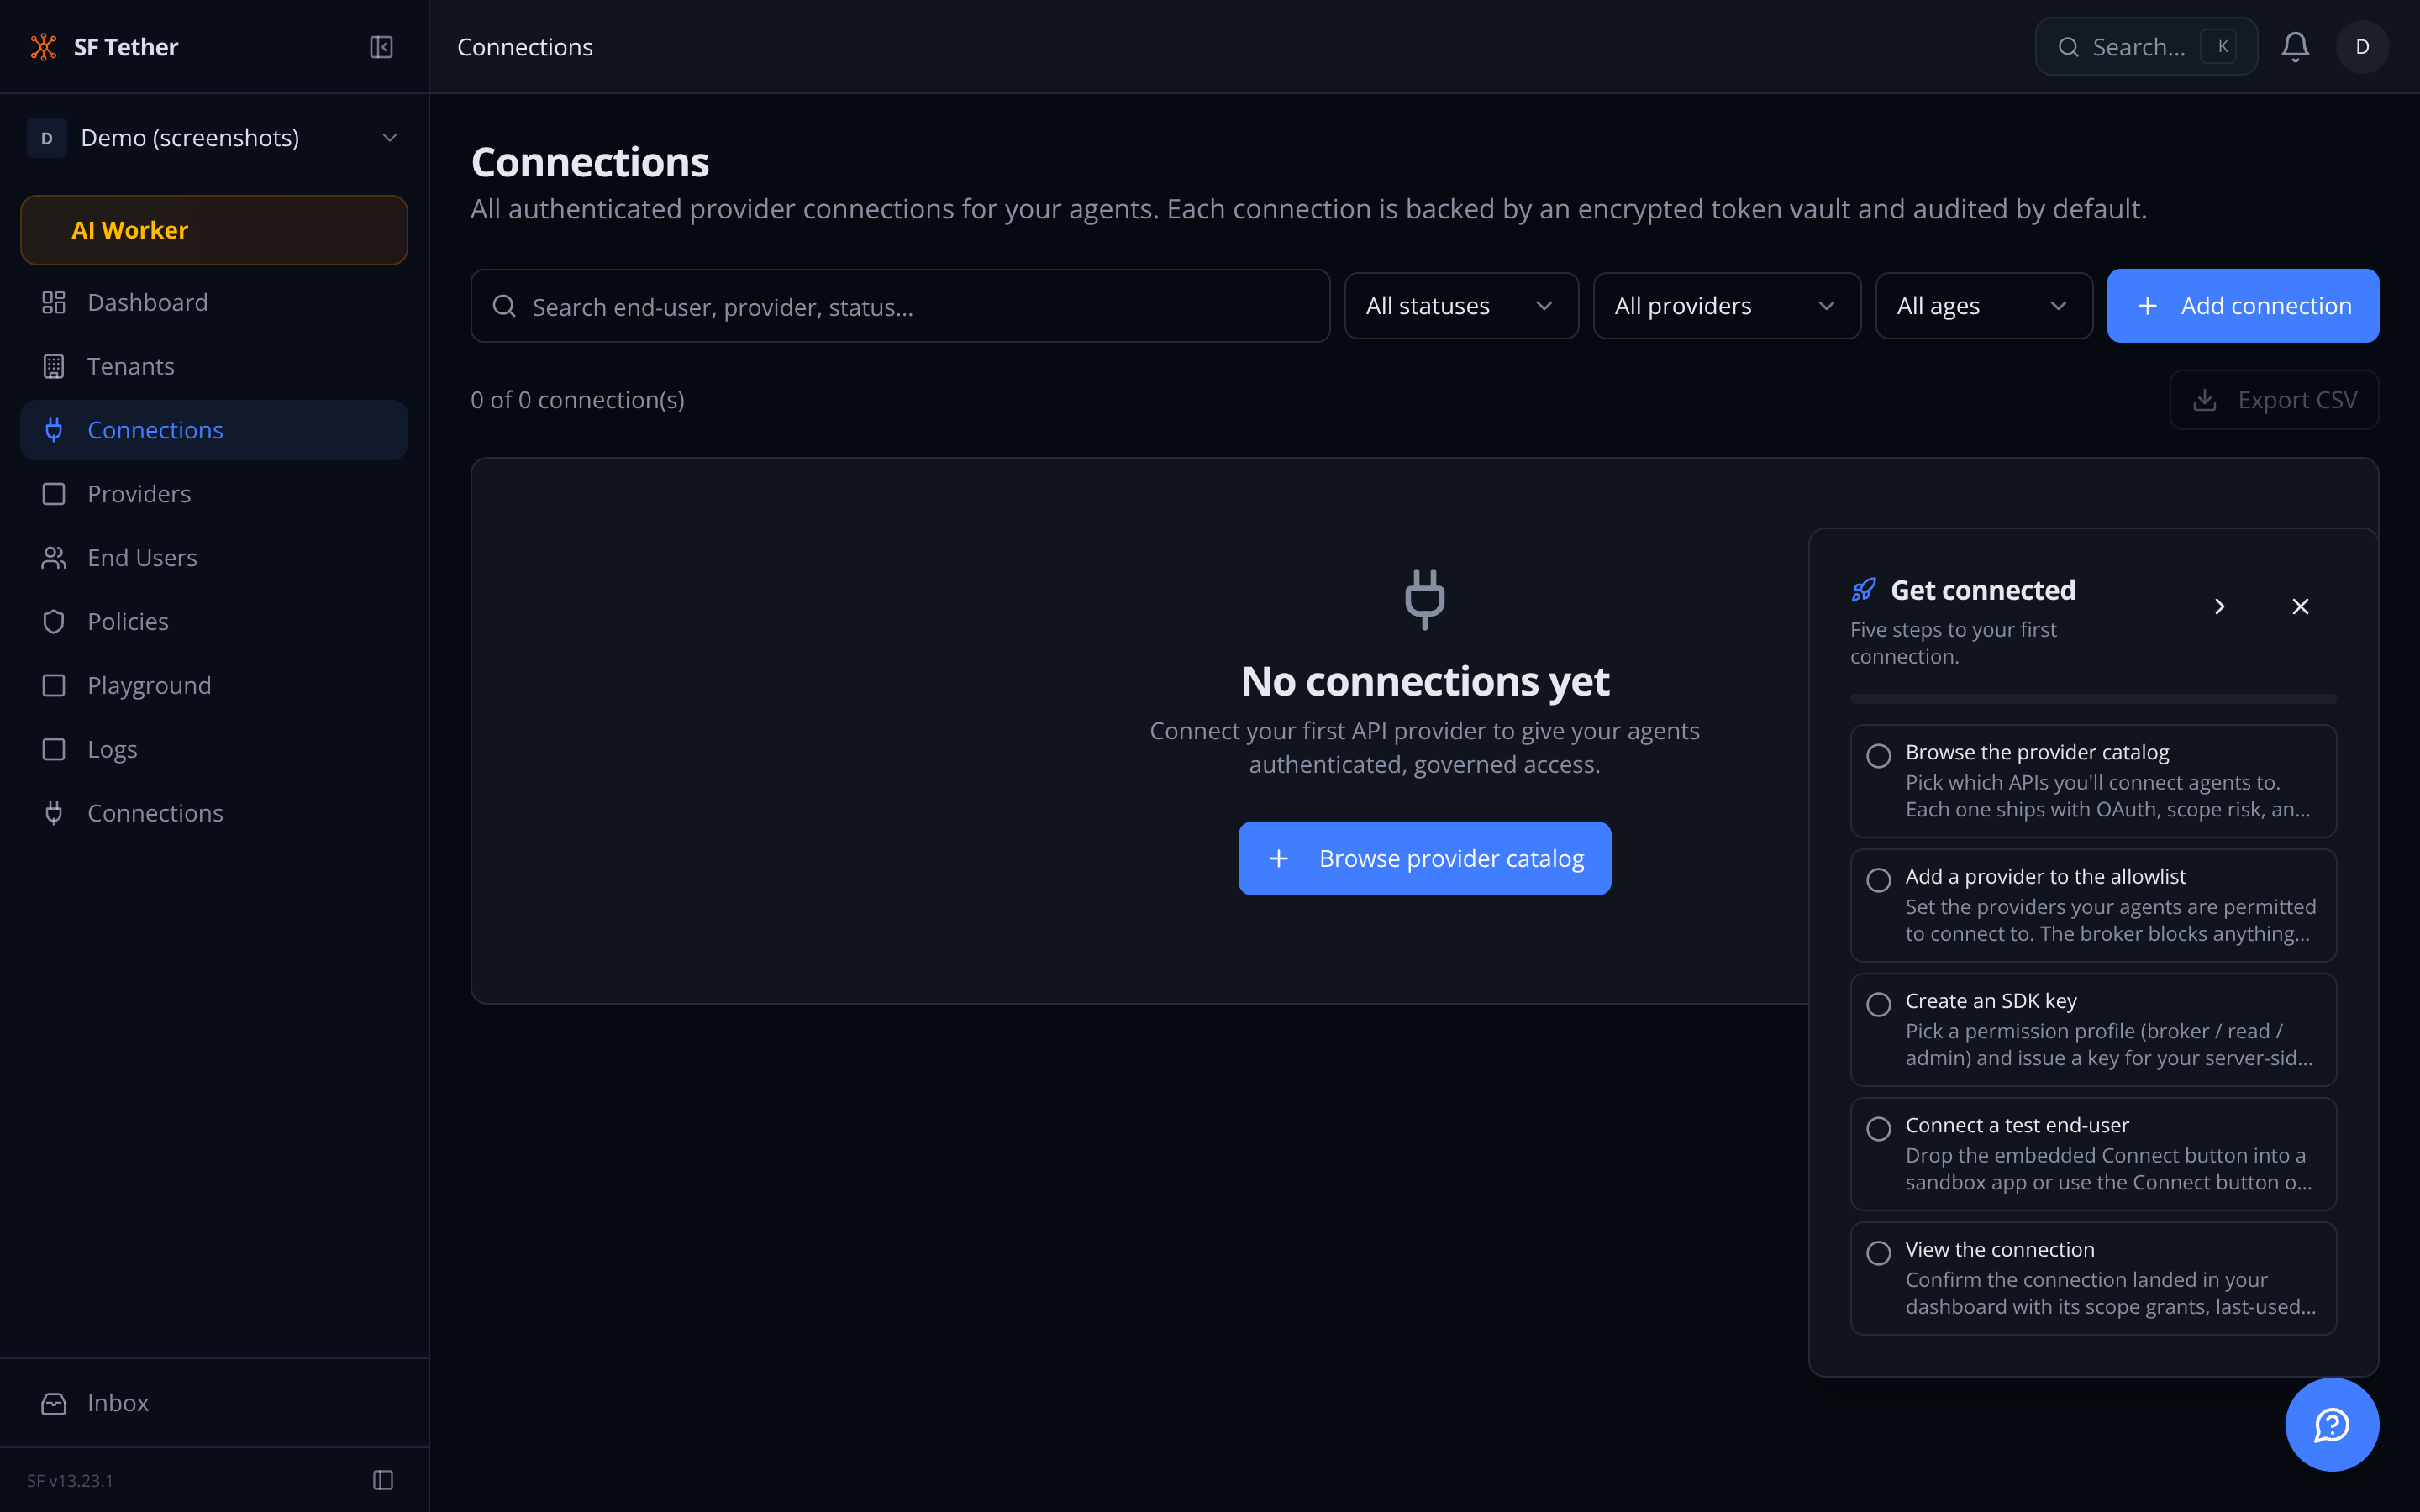
The connections dashboard shows every end-user × provider pair in your org — status, scopes held, last refresh time, error count, and broker issuance history — in a virtualized table that handles 10,000+ rows without flinching. Bulk-revoke, force-refresh, or export to CSV in one click.
Filter by status, provider, or age
Click any row for the per-connection detail & timeline
Bulk revoke or force-refresh selected connections
[ PROVIDER CATALOG / ACTIVE ]
25+ providers. Pre-wired. No dev portal.
The catalog ships with OAuth 2.0 endpoints, scope metadata, and PKCE-correct flows for every provider below. The Nango provider YAML (400+ providers) syncs daily — new entries arrive via automated PR.
Entra ID / multi-tenant OAuth with tenant-scoped endpoints and token refresh.
Slack
User token track — channel and DM scopes enforced per policy with full refresh.
GitHub
OAuth Apps supported. Repository, issue, and PR scopes with automatic expiry tracking.
Notion
Page and database access. Scopes presented in plain English on the consent screen.
Linear
Issue and project scopes. Typed arctic client ensures PKCE is wired correctly.
Salesforce
Instance URL resolved per org. Refresh handled across sandbox and production endpoints.
HubSpot
CRM and marketing scopes. Webhook events fire on connection state changes.
Jira & Asana
Project management scopes. Connect end-users in under 60 seconds via the embeddable widget.
Also in the catalog: Shopify, Zendesk, Intercom, Dropbox, Box, Twilio, SendGrid, Airtable, Figma, Discord, Zoom, Mailchimp, X (Twitter), GitLab. The daily catalog sync pulls new entries from the Nango provider YAML and opens a review PR — you approve, it lands.
Add providers to your org's allowlist from the catalog. Paste your OAuth client credentials once — Tether stores them encrypted; your agents never see them.
STEP 02 — CONNECT
End-users authorize once
The embeddable Connect button opens the provider's OAuth screen with exact scopes shown in plain English. After consent, the encrypted token is vaulted automatically.
STEP 03 — BROKER
Agents call one endpoint
Your agent sends a single request to the broker. Tether checks policy, verifies the connection is active, refreshes if within 30 seconds of expiry, and returns a short-lived scoped token.
STEP 04 — AUDIT
Every issuance is logged
The logs explorer gives auditors a unified timeline — broker issuances, connection events, scope changes — filterable by provider, end-user, IP, or agent session. Export to CSV for SOC2 evidence.
console
0.0s$ tether providers add --slug google --scopes calendar.readonly,drive.file
0.2s✓ google added to allowlist. OAuth endpoints configured.
0.4sclient_id + client_secret encrypted at rest (AES-256-GCM).
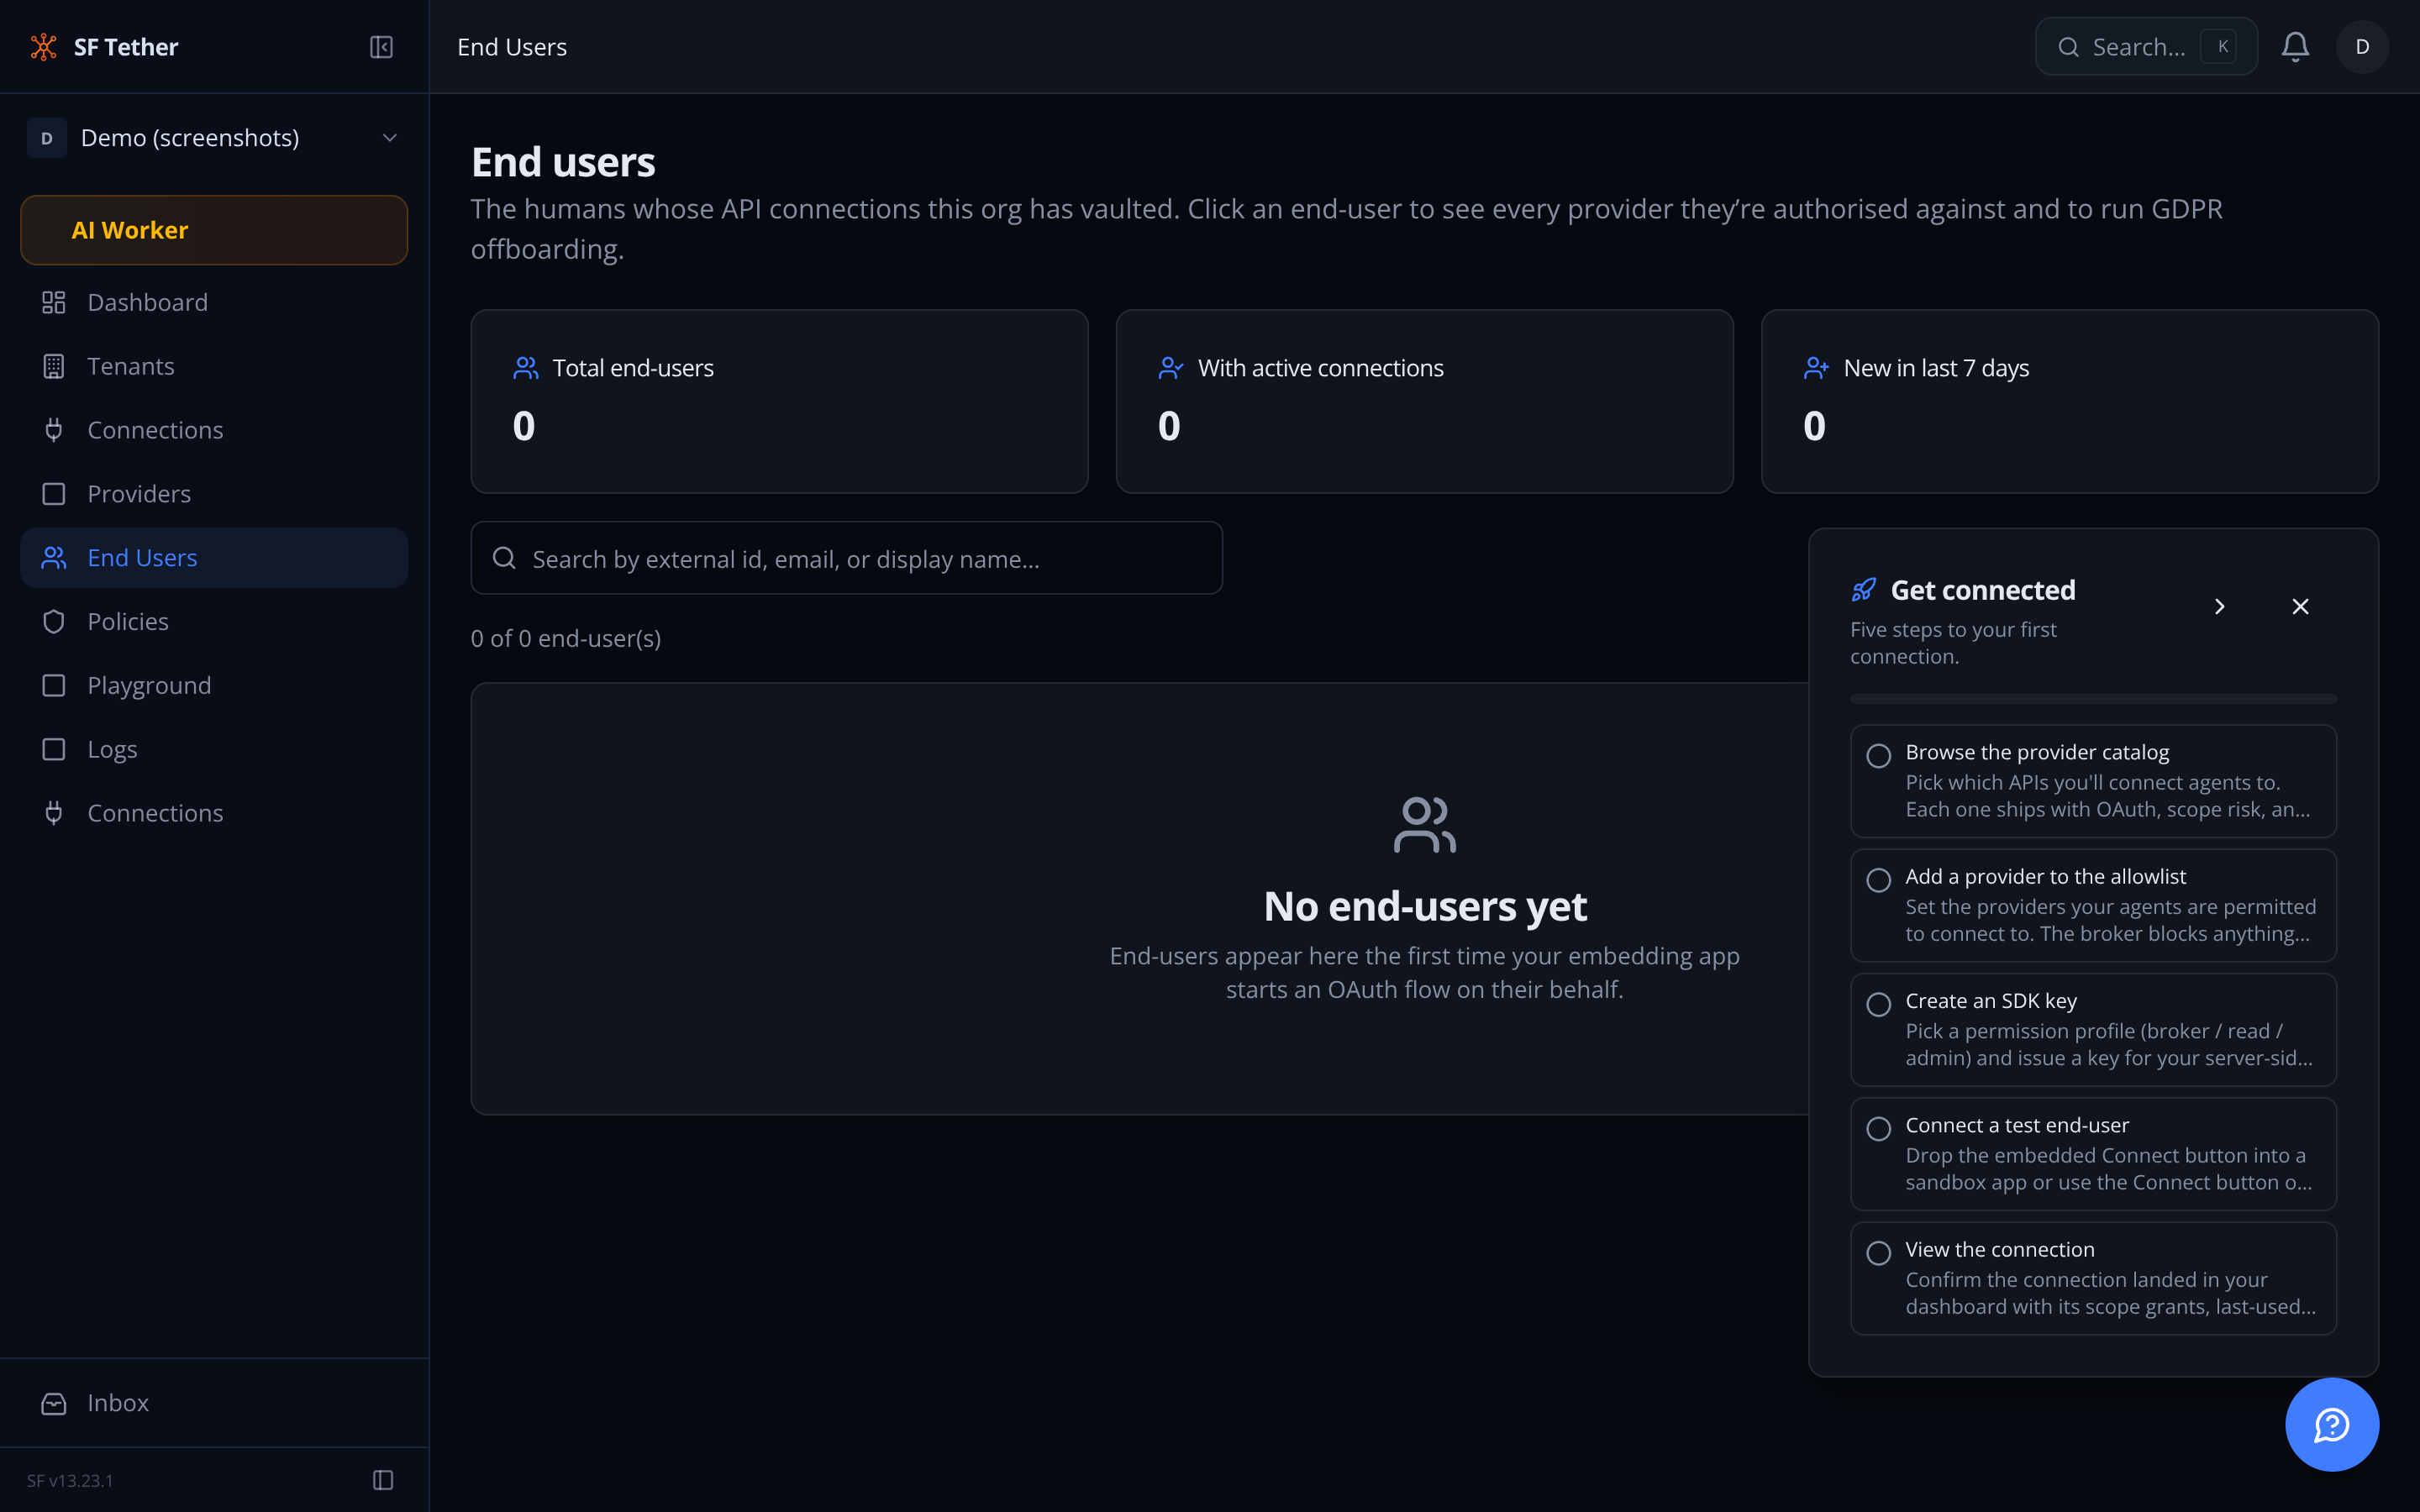
The end-users directory maps your app's user IDs to every provider connection they hold. GDPR offboarding is a single click — 'Revoke all connections for this user' calls each provider's revoke endpoint, zeros the credential row, and emits a signed webhook event.
External user ID is the join key — no schema changes in your app
Per-user view lists every active, expired, and revoked connection
Bulk offboarding for GDPR right-to-erasure flows
[ GOVERNANCE / POLICY ENGINE ]
Agents ask only for what they're allowed to have
Scope policy runs at connection creation AND at every broker token request — even if you tighten a policy after a connection is already active. Agents that ask for out-of-scope access trigger a consent flow, not an error that breaks your product.
Provider allowlist
Toggle providers on or off per org. Agents can't initiate connections to providers outside the allowlist — rejected at the start endpoint before any OAuth redirect fires.
Scope-level rules
For each scope, choose allow, deny, or require human approval. Risk levels from the catalog are shown as color-coded badges on the consent screen.
Rate limits per connection
Per-connection and per-API-key issuance caps enforced by the KV-backed middleware. A runaway agent loop can't burn provider quota or your billing.
[ SDK / AGENT INTEGRATION ]
Five lines of code. A valid token. Every time.
The broker endpoint accepts your SDK key, the user reference, the provider slug, and the scopes you need. It returns the provider's real access token — short-lived, least-privilege, and logged. The quickstart page pre-fills your actual key so the first token takes under five minutes.
Node, Python, and Go snippets in the quickstart
MCP tool surface for Claude, OpenAI, and any MCP-aware framework
REST API for server-to-server provisioning and bulk end-user creation
Embeddable Connect button ships as a drop-in React component
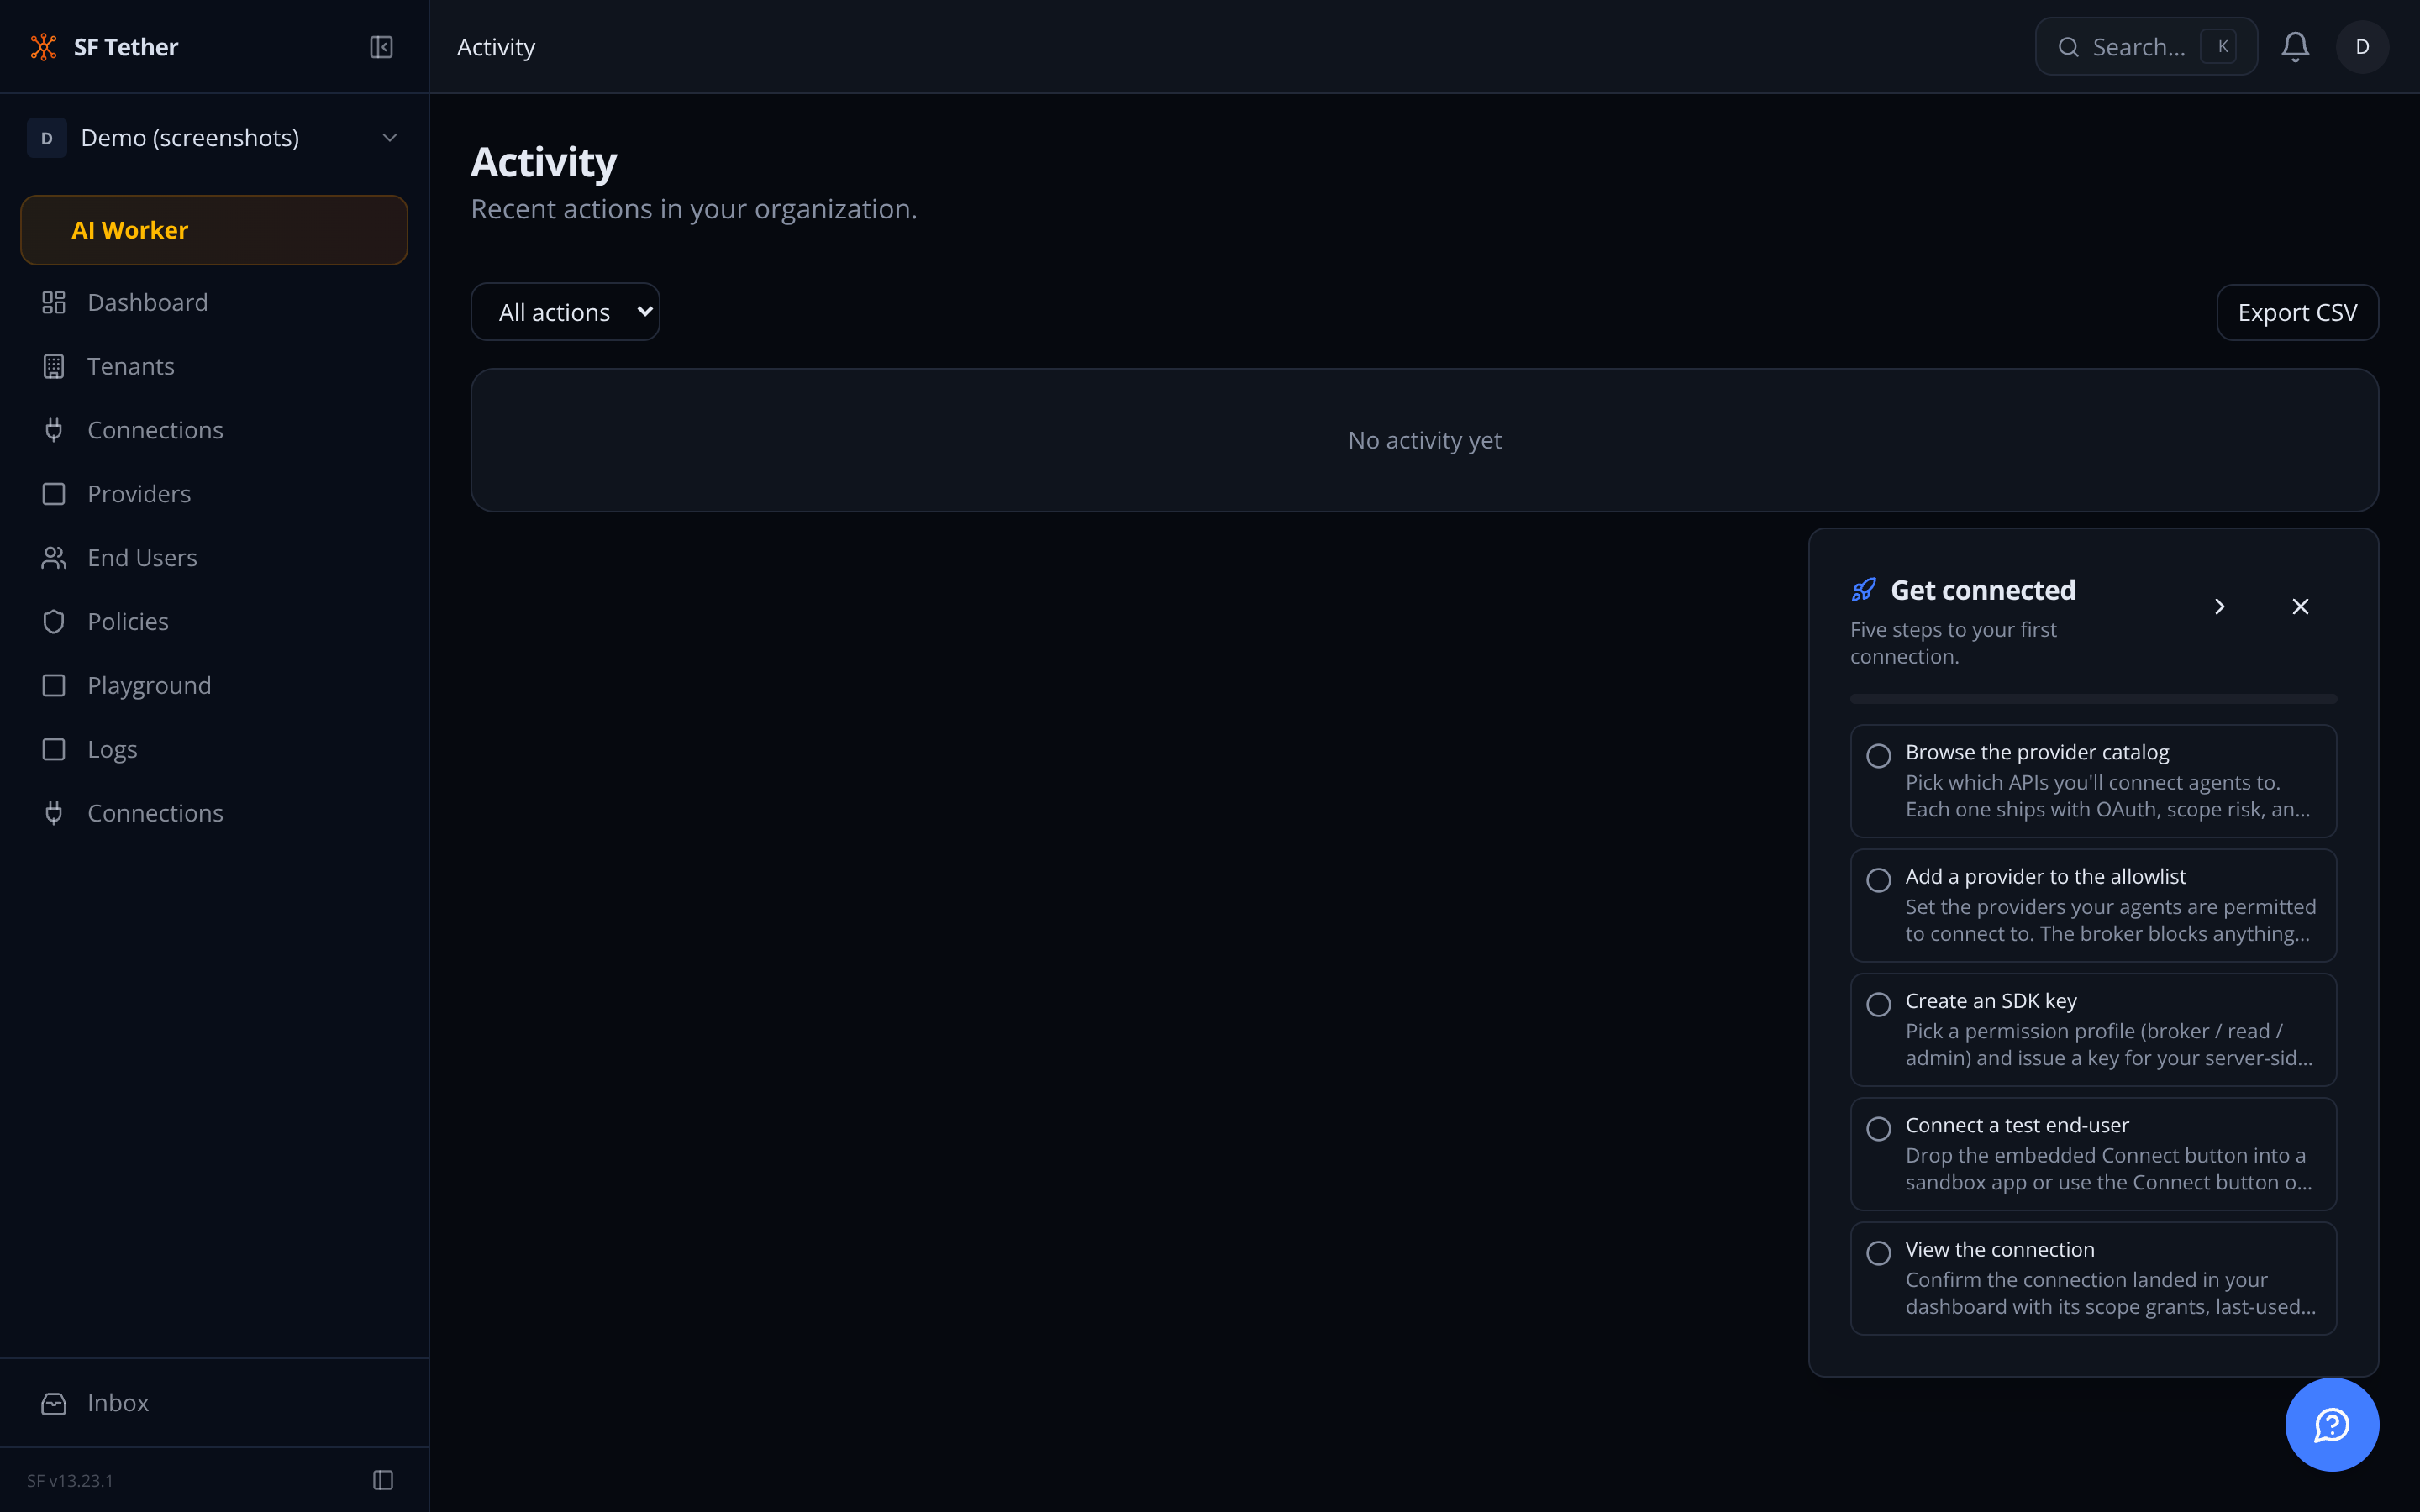
Every token issuance, scope change, and connection event lands in append-only tables — UPDATE and DELETE revoked at the database role level. The logs explorer gives auditors a filterable timeline they can export to CSV or JSON without engineering involvement.
Unified timelineConnection events and broker issuances in one virtualized view — filter by event type, provider, IP, or agent session.
Append-only schematether_connection_events rows are 7-year retention; broker logs 90-day hot. Neither can be altered by the application role.
Outbound webhooksHMAC-signed events for every connection state change — connection.authorized, connection.expired, broker.token_issued — delivered to your endpoint.
Data exportFull org dataset — connections, end-users, scope grants, audit trail — bundled into a signed zip for SOC2 evidence or GDPR portability.
Encryption happens inside the Drizzle column type — no application code path can accidentally write plaintext. A raw SELECT in the database returns ciphertext; decryption requires the correct row context binding.
PKCE-correct for every flow
The code verifier never travels through the browser. It's stored server-side and deleted on first use. State JWTs are signed and replay-protected via a per-request nonce ledger.
Single-flight refresh
Concurrent broker calls for the same connection serialize through a Postgres advisory lock — exactly one refresh fires, no duplicate tokens, no race conditions under load.
Credential reveal is audited
Admin token reveals are gated behind a permission check and logged as admin.credential_revealed events. Token-shaped strings in error messages are automatically redacted before they reach logs.
[ PRODUCT / 72 FEATURES SHIPPED ]
The infrastructure layer your agents were missing
25+
Providers in the catalog
72
Features shipped
<50ms
Broker p50 (fresh token)
1 SDK call
To a valid, scoped token
Common questions about integrations
Your agent calls a single endpoint — POST /api/broker/token — with the end user's reference and the provider you need. Tether resolves the stored connection, checks it's active, verifies the requested scopes are within what the user consented to, auto-refreshes the credential if it's expiring within 30 seconds, and returns a short-lived provider access token bound to that agent session. On a warm connection with a fresh token, this resolves at under 50ms (p50). The full audit trail — scopes requested, scopes issued, latency, outcome — is written on every call.
Scope policy is enforced twice: at the moment a connection is created and on every single token issuance, even if you tightened the policy after the connection was made. If an agent asks for scopes the connection doesn't hold, Tether doesn't silently drop them — it creates a scope upgrade request, notifies the end user via email with a re-auth link, and returns a requires_consent response with a consentUrl so the agent can handle it gracefully. Org-level provider allowlists and per-connection rate limits (backed by Vercel KV) add additional layers; a runaway agent loop that exceeds the rate cap gets a 429 with a Retry-After header, not silent failure.
Tokens are encrypted at the Drizzle column-type layer using AES-256-GCM before they ever reach Postgres. Every ciphertext is context-bound to the specific table and row it belongs to, so a leaked ciphertext for one row cannot be replayed against another. A raw SELECT in the database returns ciphertext, not plaintext — decryption only happens through the application's typed schema layer. Admin credential reveals in the dashboard are gated to admin roles and log an admin.credential_revealed audit event every time. A rotateAllCredentials operation is available for key rotation drills.
Every connection lifecycle event (created, authorized, refreshed, revoked, error, scope change) is written to an append-only tether_connection_events table with a 7-year retention policy. Every broker token issuance — including scopes requested, scopes issued, latency, and outcome — is written to tether_broker_issuance_log, retained 90 days hot. Both tables are enforced append-only at the database permission layer: UPDATE and DELETE are revoked from the application role. The dashboard's log explorer lets you filter by event type, connection, end user, provider, IP, time range, and agent session, then export the filtered slice as CSV or JSON. An org-level data export compiles the full dataset — connections, end users, scope grants, and the complete audit logs — into a signed, zipped bundle for SOC 2 reviews or GDPR data-portability requests.
No. Tether ships with a catalog of 25+ pre-configured providers including Google, Microsoft 365, Slack, GitHub, Notion, Linear, Salesforce, HubSpot, Jira, Zendesk, and others — each pre-loaded with OAuth 2.0 endpoints, scope catalogs, and PKCE handling. A guided setup wizard walks you through registering your OAuth app with each provider: it shows you exactly which callback URL to paste into the provider's developer portal, then stores your client credentials encrypted. For your end users, a drop-in React component — TetherConnectButton — opens the OAuth flow in a popup and fires onSuccess/onError callbacks. The consent screen shown to end users displays your app's branding, the provider's logo, and plain-English descriptions of every scope being requested, color-coded by risk level.
No. A background job runs every 5 minutes, finds credentials expiring within the next 15 minutes, and refreshes them proactively — so agents almost never hit an expired token. When a refresh fails permanently (the user revoked access at the provider), the connection transitions to expired, a banner appears in your dashboard with a fix-now CTA, an email goes to the end user with a magic re-auth link, and your server receives a connection.expired webhook. The re-auth link drops the user directly into the OAuth flow without requiring them to log into your app first. You can also revoke any connection programmatically via API — including a bulk panic-revoke that zeros all credentials for an org, available as both a dashboard action and a REST endpoint.
[ EARLY ACCESS / JOIN THE WAITLIST ]
Your agents are ready. Give them the keys.
Join the waitlist and we'll reach out when your org is ready to onboard. Questions? Email us at sf-core-org-support-sf-tether@saas-factory.ai